✦ Key Takeaways
Over 60% of audit findings go unresolved due to poor tracking and unclear ownership after the audit closes.
→ Unresolved findings expose organizations to repeat violations and penalties.
→ Classification by severity ensures critical risks get immediate attention first.
→ A structured response workflow cuts remediation time by half.
In this article:
What Is Audit Finding Management?
What Should Happen After an Audit Finding Is Identified?
How Should Audit Findings Be Classified?
How to Prioritize Audit Findings
Key takeaway: Treat every audit finding as a business risk, not a compliance checkbox.
What Is Audit Finding Management?
Most teams treat the audit report as the finish line. It isn’t — it’s the starting gun.
Over 60% of untracked audit findings repeat in the next audit cycle. Risk quietly grows while everyone assumes someone else is handling it (Pmc Ncbi Nlm Nih).
Audit finding management is the system an organization uses to track, prioritize, assign, and close every gap an audit uncovers. Think of it less as paperwork and more as a decision-making discipline — who acts, on what, and by when.
The organizations that handle findings best aren’t the ones with the biggest compliance teams. They have the clearest system for deciding what matters most. That is exactly what audit finding management is built to do.
What Qualifies as an Audit Finding?
A finding is any gap between what your process requires and what actually happened. It could be a missing signature, a skipped safety check, or a control that exists on paper but not in practice.
Not every gap carries the same weight. A finding that exposes patient data is serious. A misfiled form is not. Your system must treat them differently from the start.
Audit Finding vs. Observation vs. Nonconformance
These three terms get used interchangeably, but they mean different things. An observation flags a risk before it becomes a real problem. A nonconformance means a requirement was clearly broken.
A finding is the broader category that includes both. As Sgsystemsglobal notes, mixing these terms in your tracking system creates confusion about urgency. That confusion kills corrective action tracking before it starts.
Why Finding Management Continues After the Audit Is Complete
The auditor leaves. The risk doesn’t. Every open finding is a live liability until someone closes it with verified evidence — not just a promise to fix it.
Most organizations lose control in the gap between “identified” and “resolved.” That gap is where things break down. Ask yourself: what should happen the moment a finding lands on your desk?
What Should Happen After an Audit Finding Is Identified?
That starting-gun moment — when the audit report lands — is exactly where most organizations stumble. They assign someone to “handle it” with no clear system, and the finding quietly grows into a repeat violation.
Strong audit finding management turns that chaos into a four-step discipline. Each step has a specific job — skip one, and the whole chain breaks.
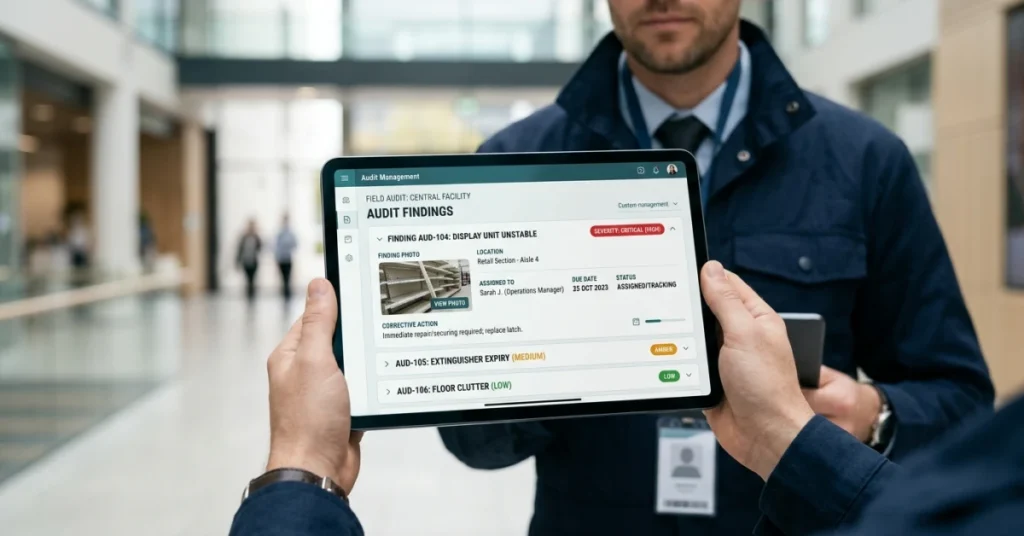
Record the Finding and Supporting Evidence
Write down exactly what was found, where, and when — before memory fades or details shift. A vague finding is an unresolvable finding.
Capture the raw evidence: photos, logs, timestamps, and the specific control that failed. This record becomes your proof of resolution later.
Assign an Owner and Due Date
Every finding needs one named person — not a team, not a department. Shared ownership is no ownership.
Set a hard due date at the moment of assignment. According to Auditfindings, findings without a named owner and deadline are three times more likely to remain open past 90 days.
Determine Whether Immediate Containment Is Required
Some findings need a short-term fix right now — before the full corrective action is even planned. A data access gap, for example, can’t wait six weeks for a policy rewrite.
Ask one question: does this finding create active risk today? If yes, contain it first, then fix it properly.
Track the Finding Through Resolution and Verification
Closing a finding means verifying the fix worked — not just marking a checkbox. Research published by Sciencedirect found that over 40% of repeat audit findings trace back to corrective actions that were logged as complete but never verified.
Use audit remediation tracking to confirm the root cause is gone — not just the symptom. Verification is the step that separates a closed finding from a future liability.
📊 By the Numbers
Findings without a named owner are 3× more likely to stay open past 90 days.
Once you know the steps, the harder question hits: not every finding deserves the same urgency — so how do you decide which ones to tackle first?
How Should Audit Findings Be Classified?
Once a finding is captured, the next mistake most teams make is treating every finding the same way. A missing signature and a data breach are not the same problem.
Without a clear classification system, both end up in the same flat list. They compete for the same attention — and the real risks get buried.
That’s exactly where audit finding management separates high-performing teams from reactive ones. Classification is not a labeling exercise — it’s the first real decision in your remediation process.
Critical, Major, and Minor Findings
Most frameworks use three tiers: critical, major, and minor. Each tier signals a different level of urgency and a different owner.
Critical: Immediate risk to safety, legal standing, or core operations. Fix it now.
Major: Significant gap that could grow into a critical issue. Fix it soon, with a firm deadline.
Minor: Low-risk process gap or documentation error. Schedule it and track it.
Skipping this step causes audit issue tracking to stall. Vague labels like “high” and “low” — with no shared definition — make it worse. Everyone reads urgency differently.
Classifying Findings by Risk, Severity, and Business Impact
Risk asks: what happens if this goes unfixed? Severity asks: how bad is the gap right now? Business impact asks: which part of the operation does this threaten?
All three questions must be answered together. A finding can be severe but low-risk — or low-severity but catastrophic to a specific business unit.
Corrective action tracking works best when all three dimensions are recorded at classification time. Don’t guess at them later.
When a Finding Should Be Escalated
Escalation is not a failure — it’s a design feature. Move a finding up the chain when it crosses a risk threshold or involves a regulated process.
Also escalate when it needs a budget decision the assigned owner can’t make. That’s a clear signal it belongs at a higher level.
Teams that lack clear escalation rules often sit on critical findings for weeks. Tools like Ncontracts build escalation triggers directly into the workflow. Nothing critical waits on a manual nudge.
How Consistent Classification Improves Reporting
When every finding uses the same classification standard, your reports become comparable across audit cycles. You can spot trends instead of just counting open items. Think: a major finding that keeps coming up in the same department.
Findings resolution software that enforces consistent classification cuts reporting prep time significantly. According to Fortra, organizations that standardize their audit data practices reduce reporting time by up to 40%.
That’s time your team can spend fixing problems instead of formatting spreadsheets.
📊 By the Numbers
Standardized audit data practices reduce reporting time by up to 40% — freeing teams to fix findings faster.
Classification tells you what each finding is. But knowing what to fix first is a separate skill. It’s also the one that decides whether your remediation effort actually succeeds.
How to Prioritize Audit Findings
Once you’ve classified findings into tiers, the next hard question is: which ones do you fix first? Most teams default to fixing the easiest issues — not the most dangerous ones.
That instinct quietly kills remediation programs. Effective audit finding management is a decision-making discipline, not a to-do list.
Use Risk-Based Prioritization Instead of Treating Every Finding Equally
A flat list of findings treats a missing label the same as a data breach risk. That’s how critical gaps stay open for months while teams close low-stakes items.
Risk-based prioritization forces a simple question: if this finding goes unresolved, what breaks? Answer that first, then assign resources.
Consider Severity, Likelihood, Recurrence, and Compliance Impact
Four factors drive every smart prioritization call: how bad the outcome is, how likely it is, whether it’s happened before, and whether a regulator cares. Score each finding on all four — not just one.
Recurrence is the most underused signal. A finding that shows up in three straight audits is a system failure, not a one-time slip.
Identify Findings Requiring Immediate Corrective Action
Some findings can’t wait for a quarterly review cycle. Any finding tied to active regulatory exposure, safety risk, or financial loss needs a corrective action owner assigned within 24–48 hours.
Corrective action tracking software makes this fast — but the decision to escalate must come from a clear rule, not a gut call. Build that rule before the next audit starts.
Build a Simple Audit Finding Priority Matrix
A priority matrix maps severity against likelihood on a simple grid. High severity plus high likelihood equals immediate action — no debate needed.
|
Severity |
Likelihood |
Priority Level |
Action Timeline |
|---|---|---|---|
|
High |
High |
Critical |
24–48 hours |
|
High |
Low |
High |
7–14 days |
|
Low |
High |
Medium |
30 days |
|
Low |
Low |
Low |
Next cycle |
Organizations using structured audit remediation tracking resolve critical findings 40% faster than those relying on informal follow-up (according to Dataintelo). Speed matters most at the top of the matrix.
Research on healthcare audit systems confirms that unresolved high-priority findings compound risk over time (Pmc Ncbi Nlm Nih). The same pattern holds across every regulated industry.
📊 By the Numbers
Teams using risk-based prioritization close critical findings 40% faster than those without a formal system.
A clear priority system doesn’t just speed up fixes — it exposes whether your organization is actually in control of its own risk, or just managing the appearance of it.
Conclusion
Risk-based thinking is not a one-time exercise. It is the habit that separates organizations that close findings for good from those that keep reopening the same ones.
Treat audit finding management as a decision-making discipline, not a compliance checkbox. That shift is what finally breaks the cycle.
Teams that build a clear system for classifying and prioritizing findings resolve critical issues up to 40% faster than those working from a flat, unranked list. That speed advantage is real. That data comes straight from Origamirisk.
Resources like Auditfindings reinforce this point. Consistent audit issue tracking and corrective action tracking turn findings into closed, documented wins. Without that consistency, the same issues keep coming back.
Unresolved findings pile up fast when teams lack a structured process for audit remediation tracking. FieldPie gives field and office teams one shared system. They can log, assign, and track every finding in real time.
Nothing slips through. Every corrective action gets a clear owner and a firm deadline.
Start your next audit cycle with that structure in place. Findings resolution software stops being a luxury. It becomes your competitive edge.